Swiss intelligence
Swiss intelligence inquiry closes many data-leak questions but leaves Kaspersky issue open
Switzerland’s defence ministry says investigations into incidents involving the Federal Intelligence Service’s former cyber unit have largely clarified the alleged data leaks and that earlier recommendations have generally been implemented. Questions about possible cooperation with Russian cybersecurity firm Kaspersky remain unresolved and have been referred to police.
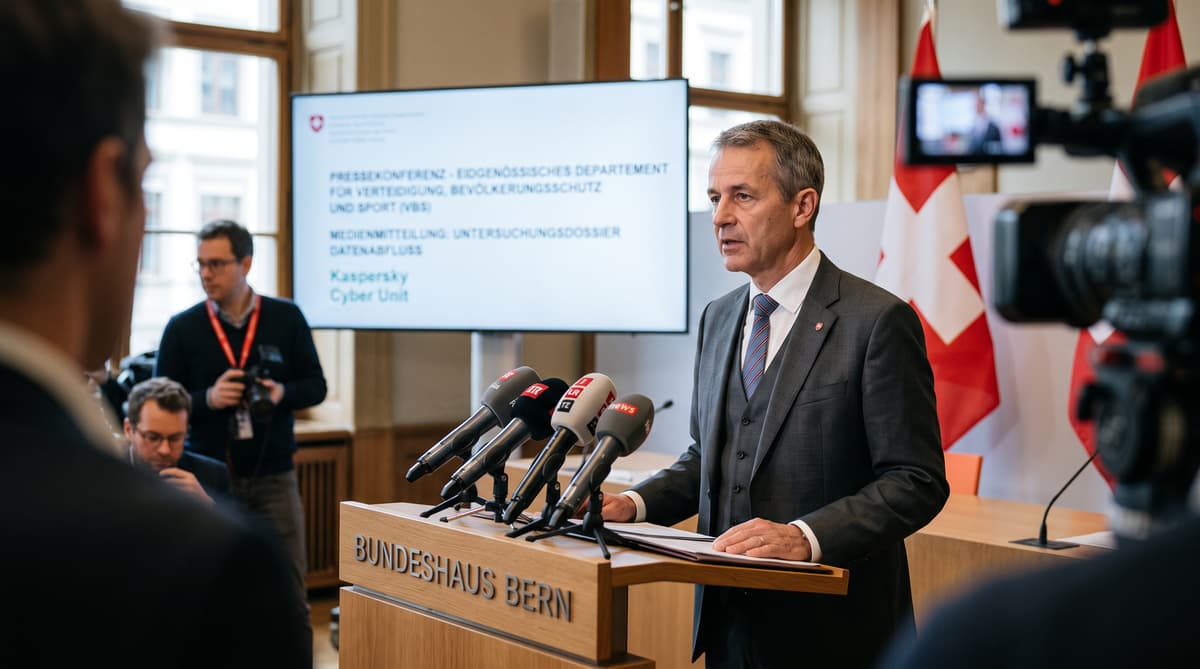
Switzerland’s defence ministry says a series of reviews has largely clarified the crisis surrounding the former cyber division of the Federal Intelligence Service, while one sensitive line of inquiry remains open. The unresolved issue concerns alleged cooperation with Russian cybersecurity company Kaspersky and has been referred to police and the Office of the Attorney General.\n\nThe ministry’s assessment covers incidents and reports that accumulated over more than two decades. The former FIS cyber unit had handled such matters since 2001, including allegations that Swiss intelligence data was transferred through Kaspersky to Russian intelligence services. Investigators also examined claims that data had been deleted.\n\nThe findings provide the FIS with a measure of institutional relief. The ministry said the incidents had been “sufficiently clarified” and that recommendations made in earlier reports had been implemented “in principle”. That conclusion does not close every legal or factual question. The Kaspersky allegations remain under investigation, leaving the most politically sensitive part of the affair outside the ministry’s final assessment.\n\nFor Swiss security authorities, the case now moves along two tracks: administrative lessons appear largely addressed, while the possible relationship with a Russian-linked technology provider awaits the outcome of a criminal investigation.
Four Reviews Test Intelligence Data Handling
Four separate review processes examined the former cyber division: one internal inquiry, two external inquiries and an audit by the supervisory authority. The breadth of that process reflects the seriousness of allegations involving a federal intelligence service and the handling of sensitive information.\n\nThe reviews examined reports of data transfers, alleged links involving Kaspersky and claims that information had been deleted. Their conclusion was limited but significant: investigators found no evidence of “large-scale” data deletion. The wording leaves room for questions about individual incidents or narrower failures, but it rejects the broadest version of the deletion allegations described in the ministry’s statement.\n\nThe defence ministry also said recommendations from earlier reports had generally been implemented. The qualification “in principle” matters because it describes the formal response to identified weaknesses, rather than declaring every operational concern settled. The ministry did not publish a detailed breakdown of each recommendation in the material available for this report.\n\nThe result is an official finding that narrows the dispute. It establishes that the major reviews did not substantiate large-scale deletion, while preserving the possibility that specific conduct or procedures still require scrutiny. That distinction will remain important as prosecutors examine the Kaspersky-related allegations separately.