cybersecurity
Cyberattack on Bern pension-fund software supplier raises data concerns
A cyberattack on a software provider used by Bern’s pension funds has raised concerns about the possible exposure of sensitive information, even though there is currently no evidence of data theft.
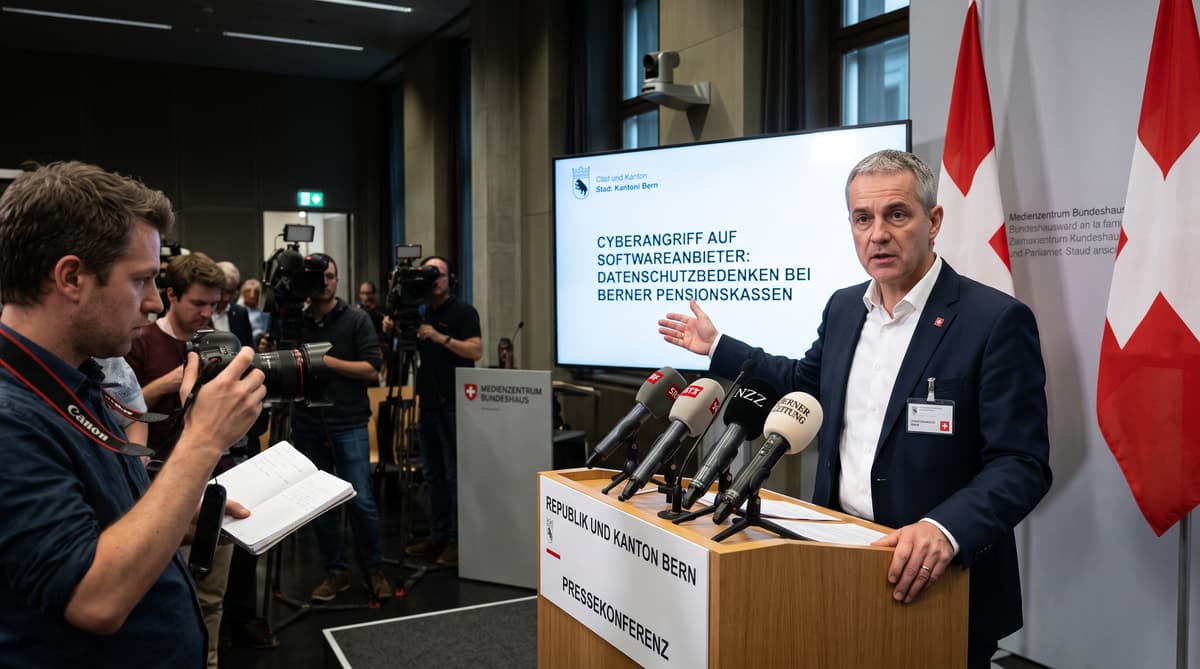
More than 91,000 people are linked to the two affected funds. A cyberattack on an external software provider used by the Bern Pension Fund and the Bern Teachers’ Insurance Fund has placed sensitive pension information under scrutiny, even though Bern authorities say they have found no evidence of data theft.
The attack took place at the end of September, according to a joint statement from the canton’s Department of Finance and Department of Education and Culture. The software company has not been identified. It filed a criminal complaint immediately, bringing the case before the Office of the Attorney General.
The two pension funds cover cantonal employees, staff at cantonal universities and teachers across Bern. Their published figures show more than 63,000 insured members and more than 28,000 pensioners at the end of December 2025. Those figures do not establish that all, or any, of their information was accessed. They show the potential scale of the population connected to the affected systems.
The incident comes as public institutions increasingly rely on specialist companies to administer payroll, benefits and pension records. A breach at one supplier can therefore create questions for several public bodies at once.
What beneficiaries know, and what remains unconfirmed
Bern has not confirmed that personal information left the supplier’s systems. The authorities have said they cannot completely rule out data theft while the investigation proceeds. That distinction matters for beneficiaries: the current announcement is a warning about a possible exposure, not confirmation that accounts, identities or pension records were taken.
The funds have been in contact with the relevant cantonal departments. Their public statement says they will provide further information if investigators establish that data was stolen, “contrary to all indications”. No additional details have been released about the type of attack, the systems affected or the information that may have been accessible.
Beneficiaries should rely on direct communications from their pension fund and remain cautious with unexpected messages referring to pensions, payments or personal records. They should avoid opening unsolicited links or sharing passwords and banking details in response to an email or phone call. These are general precautions, not evidence that any particular beneficiary has been targeted.
Until the investigation produces technical findings, the public record does not show whether attackers accessed files, encrypted systems or merely disrupted operations. The criminal complaint and ongoing inquiries are intended to establish what happened and whether protected information was compromised.
Investigators follow the trail through a third party
The investigation has two tracks: criminal inquiries and institutional checks. The unnamed supplier has filed a criminal complaint, and the Office of the Attorney General is investigating. At the same time, the Bern pension funds are coordinating with the canton to assess the consequences for their systems and members.
The source report does not identify a suspect, describe the method of attack or state whether the supplier’s systems have been restored. It also does not say that the pension funds themselves were directly penetrated. Those missing details will be important in determining whether the incident involved unauthorised access, data extraction, service disruption or a combination of these events.
The timing has attracted attention because a separate report published on October 8 described a supplier cyberattack and possible data breach affecting the federal pension fund Publica. The Bern case concerns different pension funds and an unnamed software provider. The reports illustrate a common dependency: pension institutions may hold responsibility for beneficiaries while relying on external companies to operate parts of their digital infrastructure.
For investigators, the technical evidence will include access records, system images and supplier communications. For beneficiaries, the decisive update will be whether the review identifies compromised personal or financial information.