Switzerland
Swiss Post e-voting system passes public security test without critical flaws
Swiss Post says ethical hackers found no critical vulnerabilities in its e-voting system during a larger-than-usual public penetration test. The article should report the six confirmed findings and explain why public testing remains important before wider use of online voting.
Swiss Post Opens the System to Attack
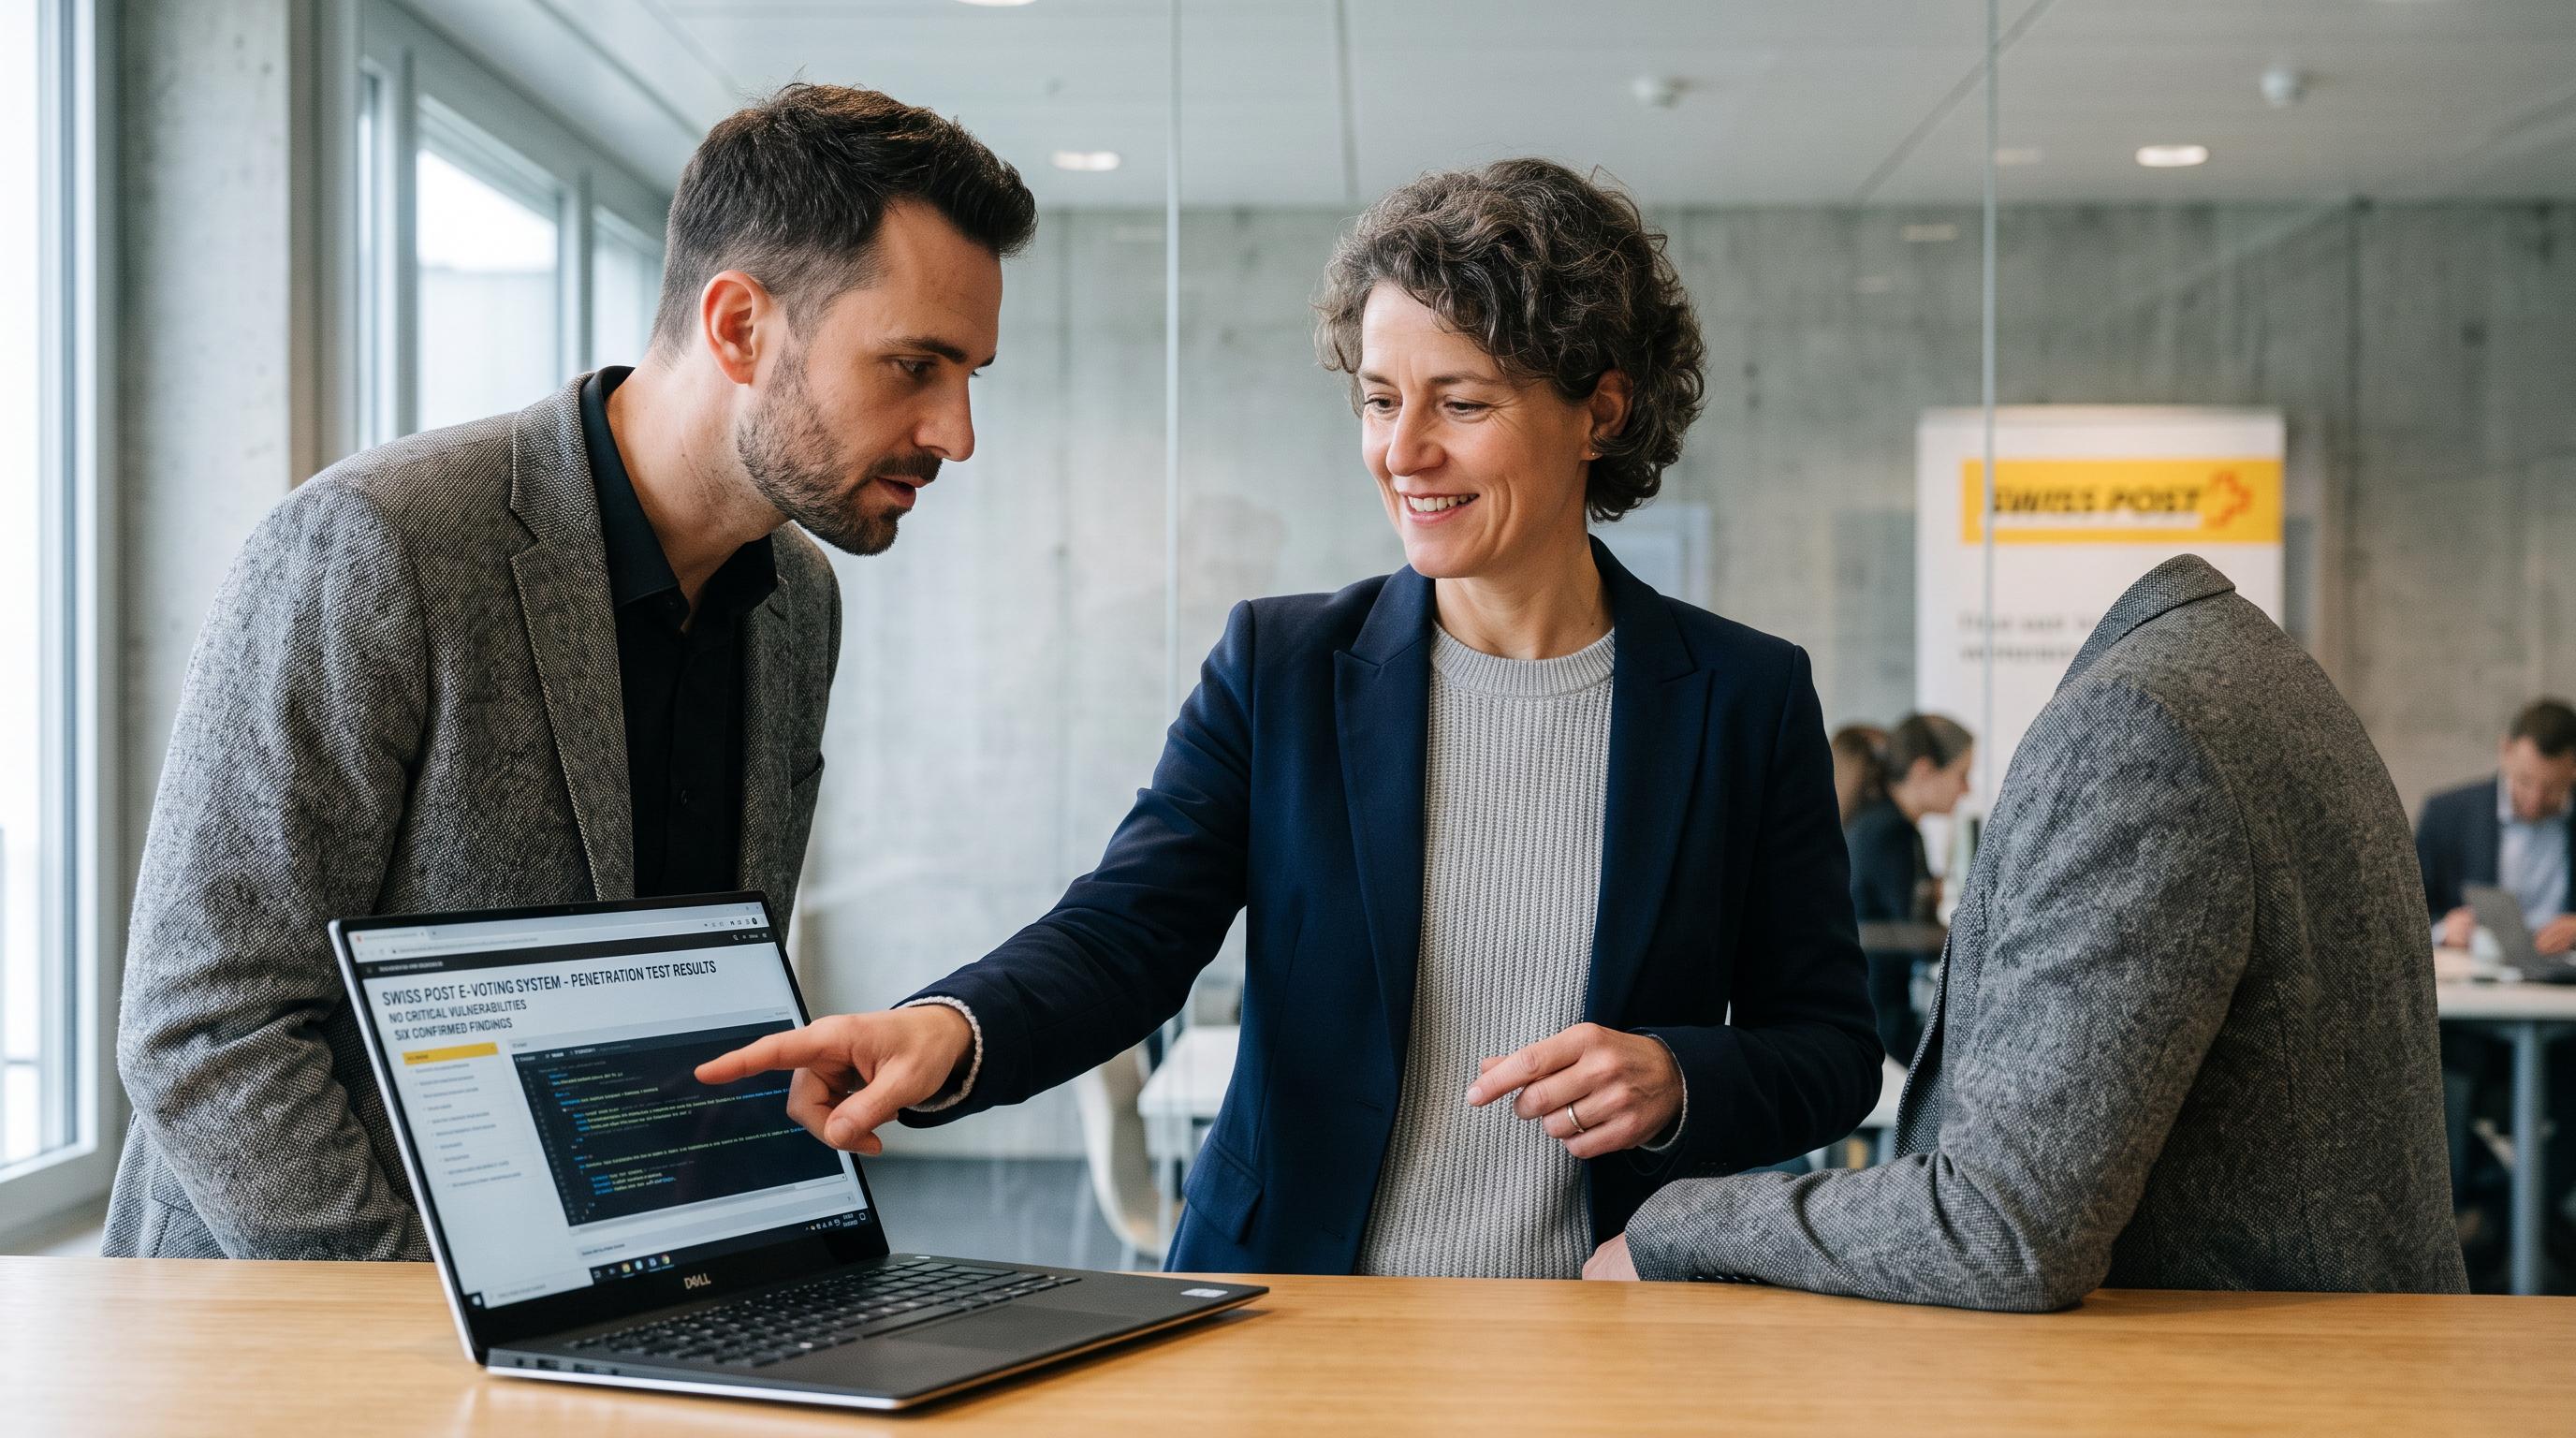
Swiss Post reported no critical vulnerabilities after a public security test that drew more than 403,000 accesses. Ethical hackers tested an identical copy of the company’s e-voting system for just under three weeks in July 2026, simulating the full voting process rather than probing a live election.
A Global Crowd Expands the Test
The 2026 test reached 5,479 IP addresses in 107 countries, compared with 2,600 IP addresses in 54 countries in 2025. The sharp increase gave Swiss Post a broader pool of researchers, systems, and attack methods to assess against the test environment.
The company received 85 reports and confirmed six findings. One ranked high severity, one medium, and four low. The source report does not identify the researchers who submitted them or provide technical details of the lower-rated issues. That limits the public assessment of how each weakness could be exploited, while the severity breakdown still gives a clear picture of the test’s outcome.
Separate Service Failure from Vote Security
The high severity finding threatened availability, not the security of ballots already cast. Swiss Post said the weakness could have compromised the voting server, potentially disrupting access to the system. The company also said the digital ballot box withstood the attacks and that the finding did not compromise vote security.
That distinction matters in an election system. A service disruption can prevent voters from using an online channel, while a breach of ballot security could affect the confidentiality, integrity, or verifiability of votes. The source does not state whether the high severity issue has been fixed, nor does it publish a technical description. Swiss Post paid around CHF 38,000 in rewards to hackers during the test, creating a direct incentive to report weaknesses through legal channels before criminals can exploit them.
Keep Scrutiny Ahead of Wider Use
Public testing gives Swiss voters evidence that extends beyond an internal security review. Researchers working independently can bring different assumptions, tools, and attack techniques to a system. Their reports also create a record of weaknesses found under controlled conditions, allowing the operator to investigate and correct them before the platform supports more ballots and more voters.
The test does not certify that the system is permanently secure. It covered an identical copy of the platform, not a live election, and the published account contains no technical details about the six confirmed findings or their remediation. Those limits should remain part of the public discussion as Swiss cantons consider where and how to expand online voting. Switzerland’s direct democratic system places particular weight on trust, auditability, and the ability to scrutinise election procedures. Repeated public tests can strengthen that scrutiny, provided Swiss Post continues to disclose meaningful results.