e-voting
Swiss Post e-voting system passes latest public security test
Swiss Post says its e-voting platform passed a three-week public penetration test without any critical vulnerabilities. Ethical hackers submitted 85 reports and the company confirmed six findings, while participation in the test more than doubled compared with the previous year.
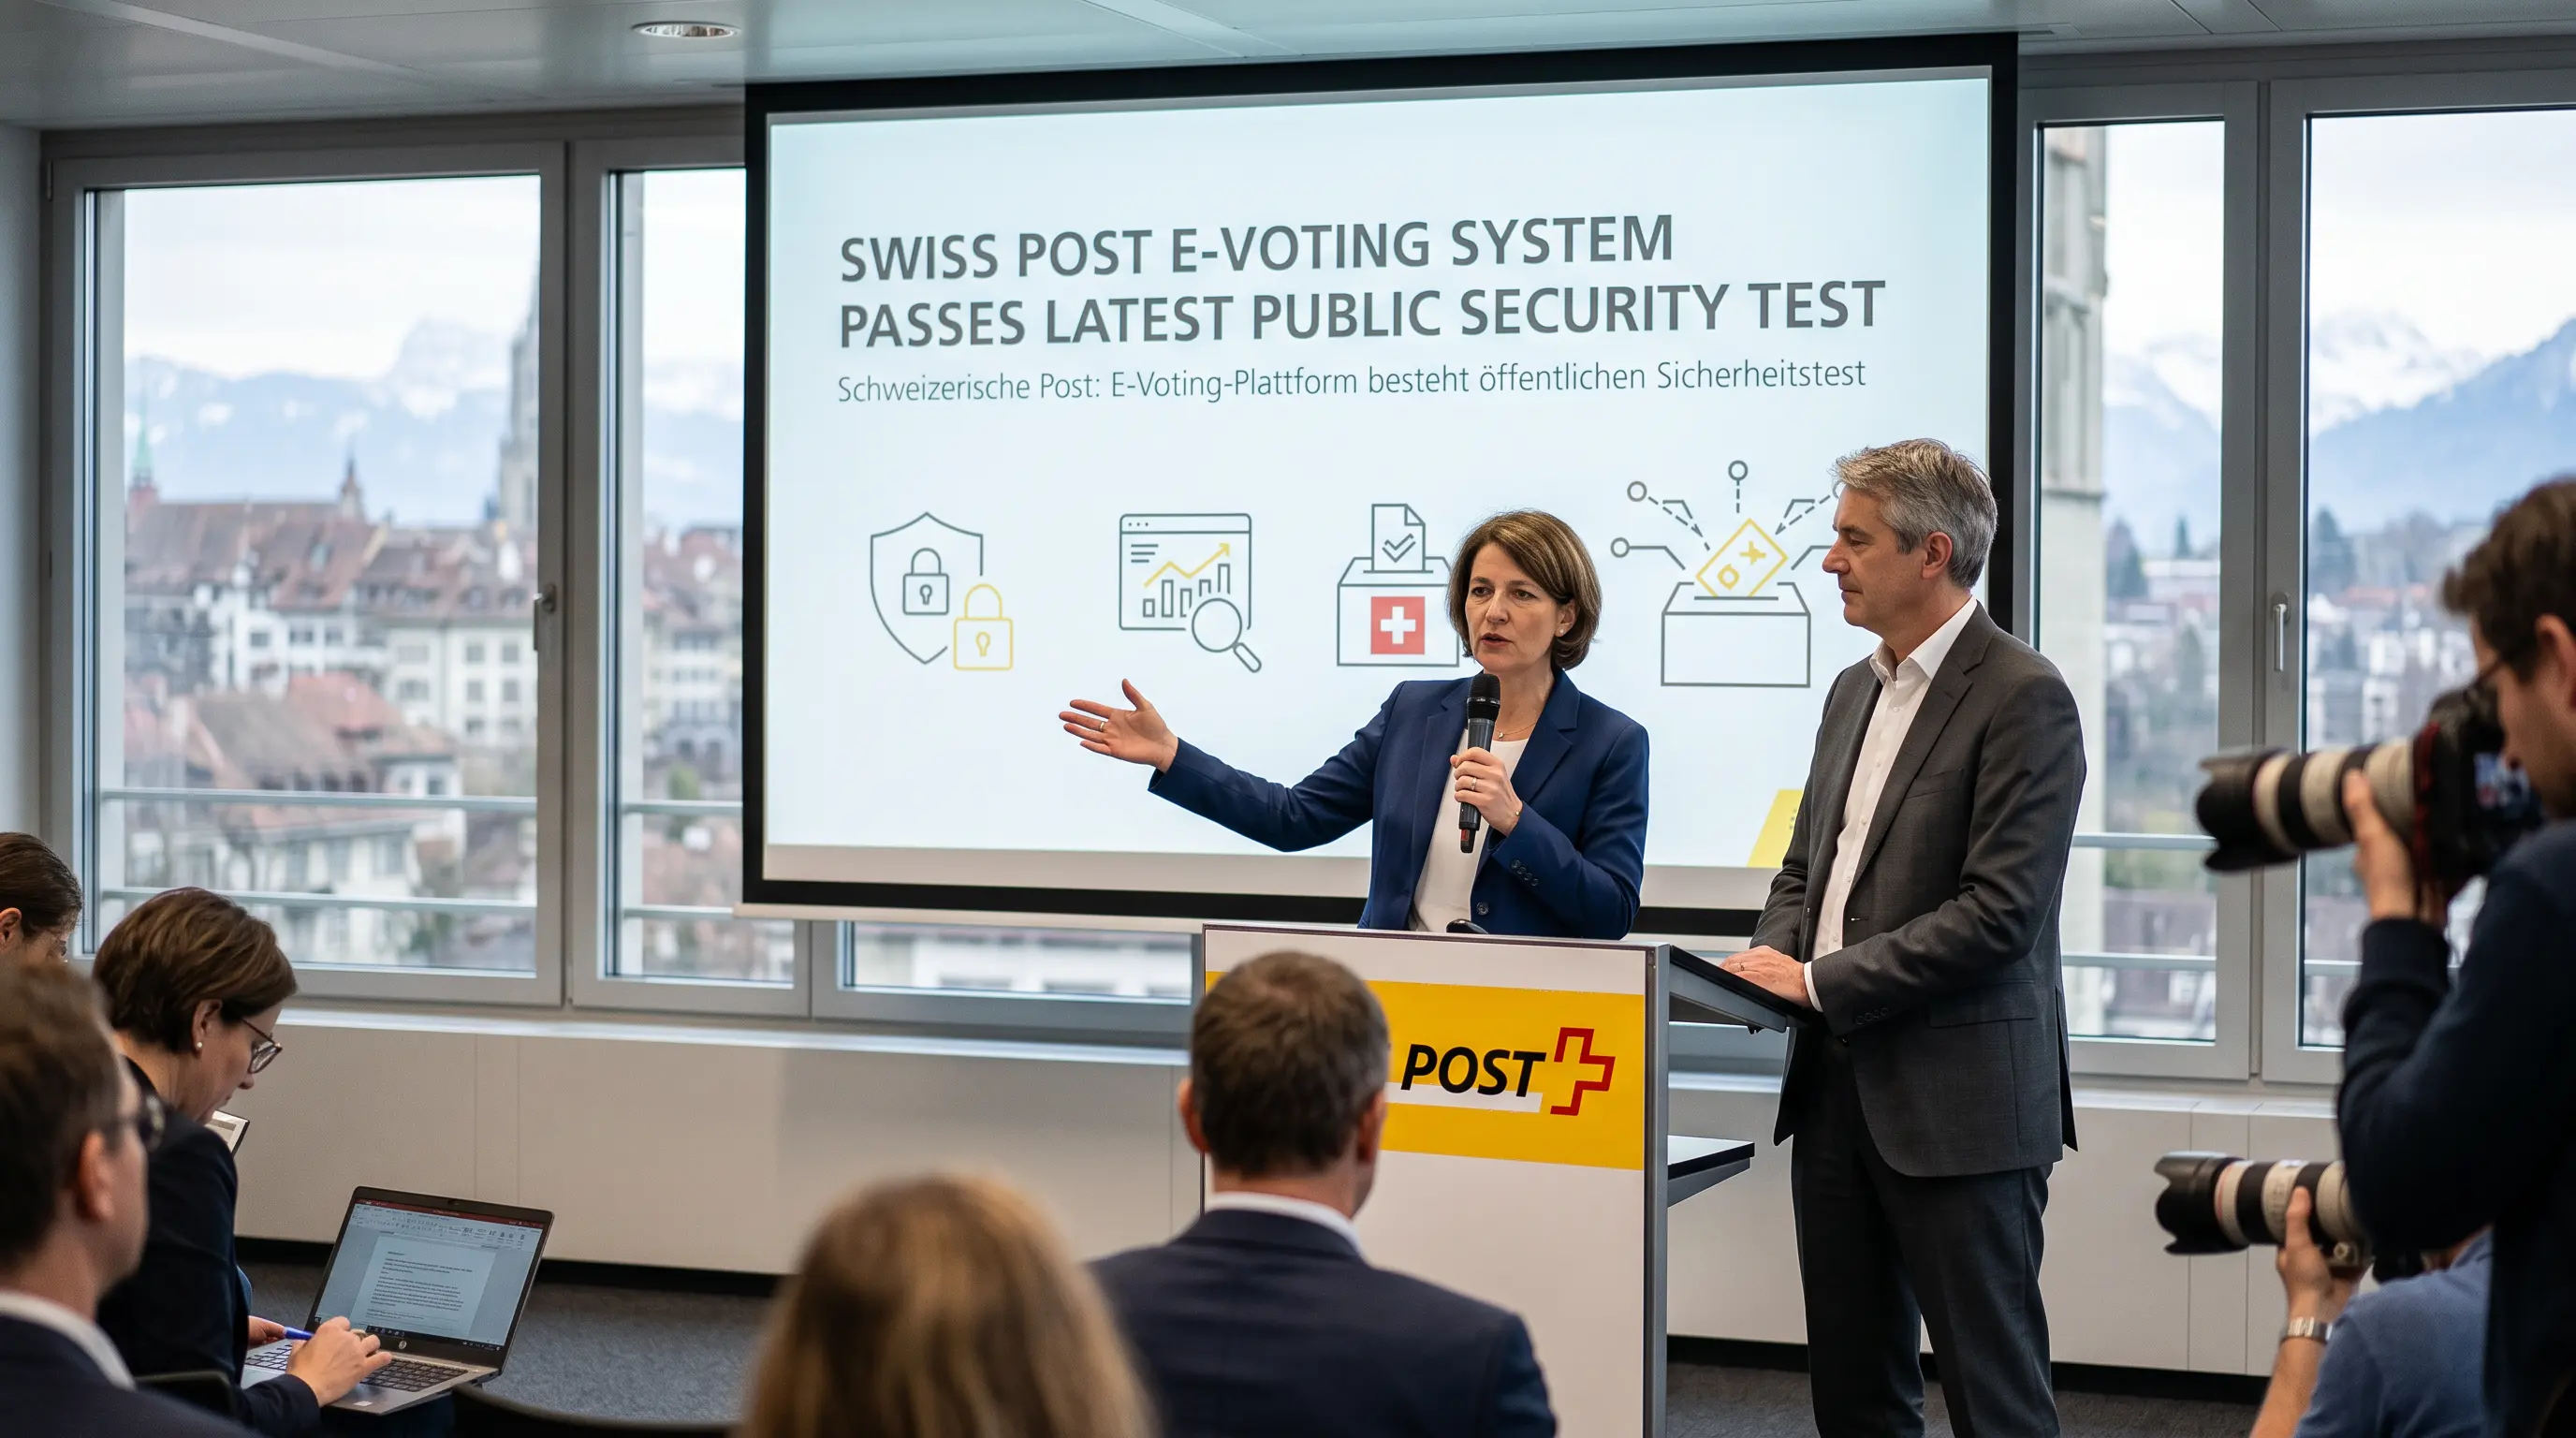
Swiss Post Clears Its Latest Digital Ballot Test
Swiss Post’s e-voting platform has cleared its latest public security test without a critical vulnerability, giving the company a fresh technical result as Switzerland expands its cautious use of digital ballots. Ethical hackers tested an identical copy of the voting system for just under three weeks in July 2026. The exercise simulated the full voting process, allowing researchers to probe the platform without interfering with a live election.
Swiss Post received 85 reports during the test and confirmed six findings. The company classified one as high severity, one as medium and four as low. Swiss Post said the high severity issue could have affected the availability of the voting server, but could not have compromised the security of votes cast.
The test therefore produced a mixed but clearly defined result: researchers found weaknesses, yet none reached the company’s critical category. Swiss Post also said its digital ballot box withstood the attacks. For Switzerland, where election security depends on public confidence as much as on technical safeguards, the distinction between identifying a flaw and exposing ballots remains central.
Global Hackers Expand the Pressure on Swiss Post
More than 403,000 accesses came from 5,479 IP addresses in 107 countries, according to Swiss Post. Participation more than doubled on the previous year’s figures, when the test drew activity from 2,600 IP addresses in 54 countries. The broader reach exposed the platform to a larger and more varied pool of security researchers.
Those numbers measure activity rather than successful attacks. An access does not automatically represent a vulnerability report, and an IP address does not identify a unique individual. They do show the scale of attention surrounding Switzerland’s electronic voting infrastructure.
The international participation also reflects the public design of the exercise. Ethical hackers received legal authorisation to seek weaknesses before criminals could exploit them. Their work ranged across the simulated voting environment, while Swiss Post assessed the reports and classified the confirmed findings according to severity.
The increased scrutiny matters because electronic voting systems must withstand both targeted technical attacks and sustained public examination. Publishing the test results gives outsiders a basis for judging the platform’s resilience, while the confirmed findings show that the process remains an active search for defects rather than a ceremonial approval.
The High Severity Finding Targeted Availability
The most serious confirmed flaw threatened availability, not ballot security. Swiss Post said the high severity vulnerability could have compromised the voting server’s availability. The company did not say that the issue could alter votes, reveal voters’ choices or undermine the digital ballot box.
That distinction is significant in an election system. A disruption can prevent access to an online voting service and force voters to use another channel or try again. A compromise of ballot security would raise different concerns, including the confidentiality, integrity and verifiability of the vote. The source report identifies the impact of the confirmed high severity finding, but does not provide technical details about the attack or the fix.
Swiss Post’s public statement also says the digital ballot box withstood the attacks despite the sharp rise in participation. The company confirmed the high, medium and low findings after reviewing the 85 reports received during the exercise.
The results leave a clear record for continued oversight. Researchers found six issues, including one that required serious attention, while the company reported no critical vulnerability. Further public reporting on remediation would help observers track how those findings are addressed before systems face real electoral demand.
Bug Bounties Keep the Platform Under Watch
Swiss Post paid around CHF 38,000 to hackers who reported vulnerabilities, turning external scrutiny into a formal part of the platform’s security process. The rewards recognise researchers who identify weaknesses under legal authorisation and give the operator an incentive to receive those warnings before a criminal actor finds them.
The latest test adds another data point to Switzerland’s gradual approach to electronic voting. Swiss authorities have treated online ballots as a controlled option alongside established voting channels, with security testing and verification forming part of the public debate. The exercise did not certify every future version of the platform, and the reported findings do not disappear simply because none was labelled critical.
Swiss Post’s result is strongest when read with those limits in view. The platform faced more than 403,000 accesses, received 85 reports and produced six confirmed findings. One issue was serious enough to threaten server availability. At the same time, the company said vote security held and no critical vulnerability emerged.
The next stage will be remediation, independent scrutiny and further tests as the system changes. For Swiss voters, cantonal authorities and election officials, confidence will depend on whether this cycle of testing and disclosure continues before each major deployment.