cybersecurity
Swiss aerospace supplier Beyond Gravity investigates targeted cyberattack
Beyond Gravity, Switzerland’s state-owned aerospace supplier, is investigating a targeted cyberattack with federal authorities and Mandiant. The article will assess the known impact, the security response and the strategic significance of the company.
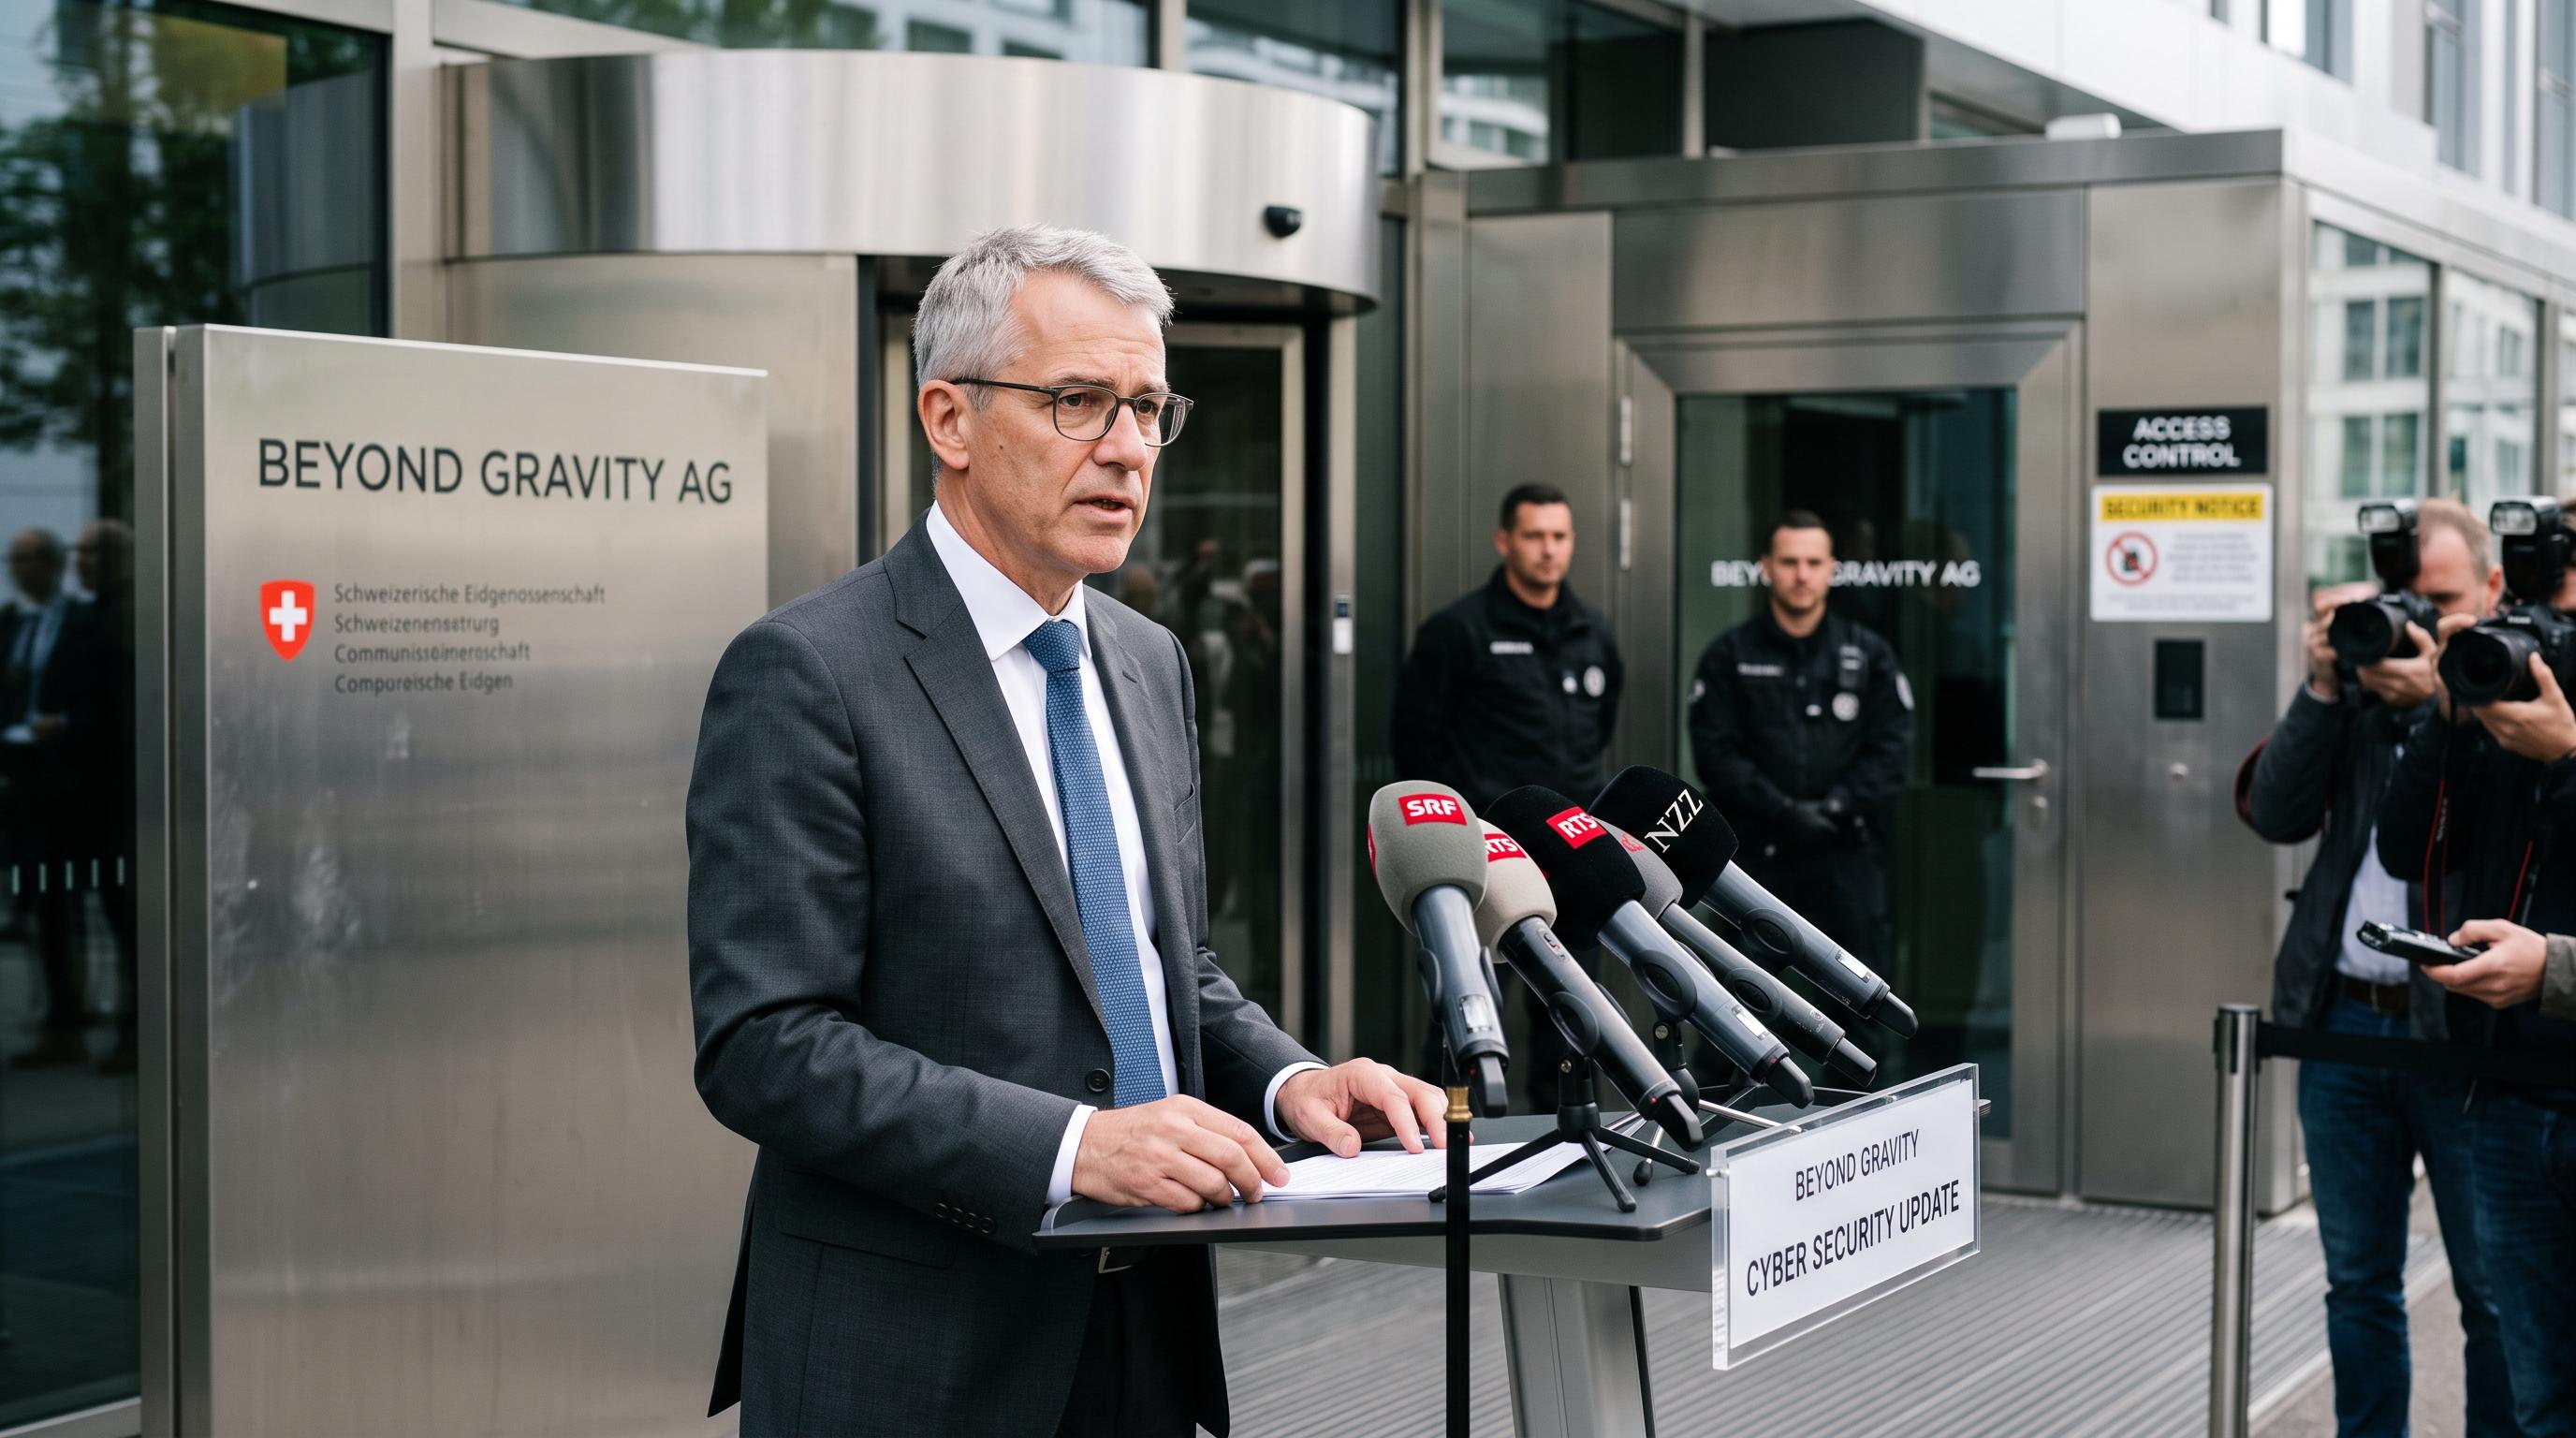
Beyond Gravity confirms a targeted attack
Beyond Gravity detected malicious activity on August 12, 2026, and has now confirmed that the Swiss aerospace supplier was the target of a focused cyberattack. The company disclosed the incident on Friday, October 2, after weeks of investigation into its IT environment.
Beyond Gravity said it believes a highly professional actor carried out the operation. The company has not identified the attacker, and it has not publicly detailed what information, systems or operations may have been affected. Those gaps matter because Beyond Gravity supplies aerospace technology from Switzerland, while remaining under Swiss state ownership.
The investigation brings together the Federal Office for Cyber Security, Switzerland’s national cyber authority, and Mandiant, the specialist security firm. Beyond Gravity has also filed a criminal complaint and strengthened its protective measures.
The public announcement provides a confirmed timeline, but no assessment of the damage. Experts are examining the attackers’ activity and conducting forensic analysis of affected devices, according to a company spokesperson quoted by the AWP news agency. The inquiry will determine whether the intrusion remained confined to individual systems or reached deeper into the company’s networks.
Investigators map the digital intrusion
Mandiant and the Federal Office for Cyber Security are tracing the intruder’s steps through affected devices. That work typically relies on digital evidence such as system logs, malicious files and records of unauthorised access, although Beyond Gravity has not disclosed which indicators investigators found in this case.
The company said specialists were specifically searching for the attackers’ activities while carrying out forensic analyses. The wording points to an investigation that is still active. Attribution remains open, and Beyond Gravity has given no public indication that a state, criminal group or named organisation is responsible.
The company’s decision to involve Mandiant adds an external specialist to the response. Federal participation reflects the wider importance of an incident involving a state-owned supplier with roots in Switzerland’s defence industry. Neither organisation has published a technical account of the suspected intrusion.
Beyond Gravity has increased its security measures and lodged a criminal complaint. Those steps create parallel tracks: investigators must preserve evidence and establish what happened, while the company must reduce the risk of further access. Until the forensic review is complete, public conclusions about stolen data, operational disruption or compromise of aerospace systems would go beyond the available evidence.
Why the state-owned supplier matters
Beyond Gravity’s ownership and industrial role give the incident significance beyond a single corporate network. Switzerland owns the company, which was separated from the defence group Ruag in 2022. Its business sits within the country’s aerospace and space technology ecosystem, an area in which Switzerland maintains a specialised position despite its small size.
That background helps explain the involvement of federal cyber authorities. A successful intrusion into an aerospace supplier could raise questions about intellectual property, engineering information, production systems and links with customers or partners. The available reporting does not establish that any of those categories were accessed. It also does not say that spacecraft, satellites or production lines were disrupted.
The company’s status places the investigation at the intersection of corporate security and public responsibility. Beyond Gravity must protect commercial information and preserve the integrity of its operations. Swiss authorities must assess whether the incident has implications for national security, critical supply chains or other organisations connected to the aerospace sector.
For now, those implications remain matters for investigators to examine. The confirmed facts are narrower: malicious activity was detected, a professional actor is suspected, and the identity and impact of the attack remain unknown.
Switzerland waits for the forensic findings
Beyond Gravity delayed its public statement for several weeks because investigators feared that premature disclosure could compromise the forensic work. The first indications appeared on August 12, while the company announced the attack on October 2. A spokesperson told AWP that “thoroughness takes precedence over speed” in cyberattack cases.
That explanation highlights the tension that follows a serious intrusion. Companies face pressure to inform employees, customers, regulators and the public. Investigators, meanwhile, need time to isolate systems, preserve evidence and understand the attacker’s movements. An early announcement can also alert an intruder that security teams have detected the operation, although the source does not say whether that occurred here.
The next phase will focus on evidence and scope. Beyond Gravity will need to establish which devices were affected, how access was obtained, whether the attacker maintained a presence and whether data left the company. The Federal Office for Cyber Security and Mandiant will contribute to that assessment, while the criminal complaint gives law enforcement a formal basis for pursuing the case.
Switzerland can expect further scrutiny of the company’s findings, particularly because Beyond Gravity remains state-owned and operates in a strategically sensitive sector.